 简体中文
 繁體中文
 English
 Français
 Русский
 日本語
 Tiếng Việt
 한국어
 Deutsch
 Español
 Italiano
 Português
 العربية
 ไทย
 Bahasa Indonesia
 Bahasa Melayu
 Türkçe
 Polski
 Nederlands
 Dansk
 Norsk
 Қазақша
Use Crazyrouter as a custom model provider in Cursor
Cursor's BYOK mode accepts any OpenAI-compatible endpoint. Enter the Crazyrouter base URL once and route chat and agent traffic through your own key with live per-token pricing.
Manual configuration
No scripts needed — three fields in the Models settings page. Verify must succeed before Cursor lets you pick the model; the most common reason it fails is a base URL with the wrong path.
Cursor → Settings → Models
OpenAI API Key:            sk-your-crazyrouter-key
Override OpenAI Base URL:  https://api.crazyrouter.com/v1
Model (add custom):        claude-opus-4-8   (or gpt-5.5, deepseek-v4-pro …)
→ click Verify
Custom keys only apply to chat/agent models. Tab completion keeps using Cursor's own models — that is a Cursor limitation.
https://api.crazyrouter.com/v1 — This tool is OpenAI-compatible and appends /chat/completions (or /responses) itself. Use the /v1 base URL exactly as shown.
Recommended models
Live Crazyrouter prices, refreshed hourly. Any model in the catalogue works; these are the ones we'd start with.
FAQ
Which base URL goes in 'Override OpenAI Base URL'?
Exactly https://api.crazyrouter.com/v1. Not the root domain, not a full /chat/completions path.
Why does Tab completion not use my key?
Cursor documents that custom API keys apply only to standard chat models; Tab and some agent features use Cursor's own models.
Which model should I add first?
claude-opus-4-8 or gpt-5.5 for agent mode; deepseek-v4-pro when you want a cheaper default for chat.
Costs jumped after switching
Give Cursor its own token with a quota cap and a narrow model allowlist, so one shared key isn't drained by agent loops.
Guides and comparisons
 Comparison
AI Coding Assistants Comparison 2026: Cursor vs Windsurf vs GitHub Copilot vs Kiro
A developer's comparison of the top AI coding assistants in 2026. Covers Cursor, Windsurf, GitHub Copilot, Kiro, and others — features, pricing
GitHub Copilot vs Claude vs Cursor: Which AI Coder Wins in 2026?
We tested GitHub Copilot, Claude, Cursor & 5 more AI coding tools. See rankings by code quality, price, and workflow fit. Updated Feb 2026.
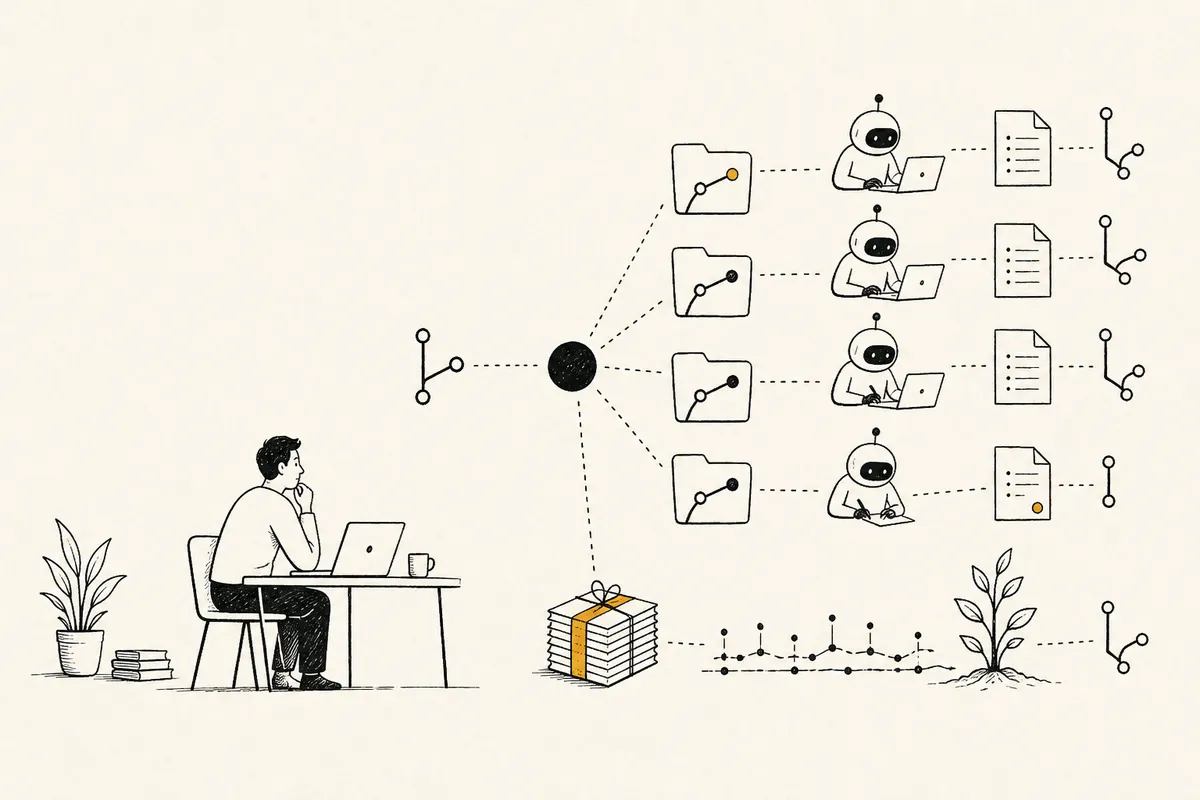 AI Coding
Background Coding Agents Without Lock-In: Recreating the Cursor Pattern with Git Worktrees
Cursor background agents are useful because they move long-running AI coding work out of your local single-branch loop. This guide rebuilds the same workflow pattern with plain git
Podcast
AI Dev Tools: The Crazyrouter Podcast
Short episodes for developers on AI APIs, gateways, cost control and coding tools.
Latest episodes
EP196 · Oct 29, 2026 · 6:53
AI API Security Posture — Turn Controls Into Continuous Evidence
A practical guide to AI API security posture: inventory exposure, verify controls continuously, protect keys and data, constrain tools, and turn security assumptions into evidence that operators can act on.
EP195 · Oct 28, 2026 · 7:21
AI API Policy Drift — Detect When Production Rules Stop Matching Intent
A practical guide to policy drift in AI APIs: version routing and safety rules, detect stale enforcement, compare intended and observed behavior, and restore control before small gaps become incidents.